Vibe Coder · Unit 13: Testing and Security · Lesson 11 of 11
Security checklist
Engineers: a pre-launch review covering headers, dependencies, input handling, logging and an agent-assisted audit.
Read the short notes and pictures.Do everything inside a blue frame.
A pre-launch review
Security work is easier as a list. Go through each area once, record what you checked, and fix what you find. An agent audit is a useful extra pass, and its findings need verifying like any other.
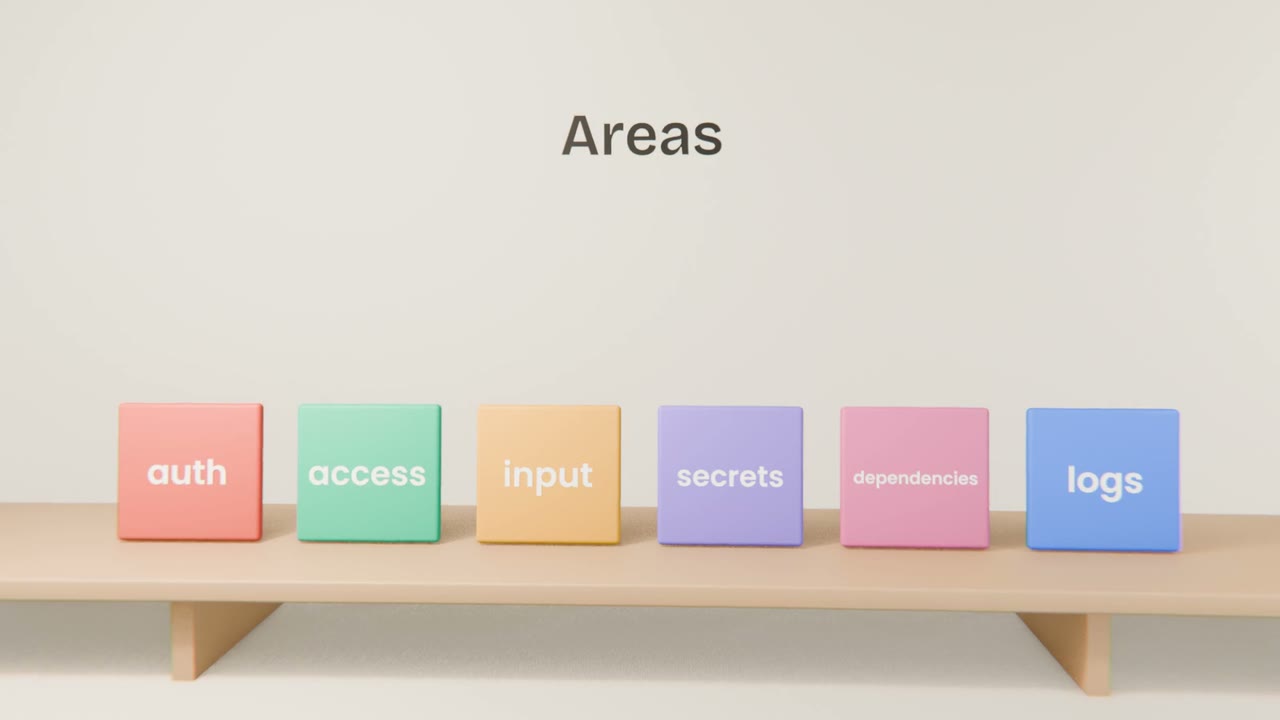
The checklist
Auth and sessions
Provider-managed, secure cookies, sign-out works.
Access control
RLS on every table, server-side checks on every route.
Input
Validated on the server, output encoded, no string-built queries.
Headers and transport
HTTPS, sensible security headers.
Dependencies
Audited and pinned.
Logging
Useful, and free of secrets and personal data.
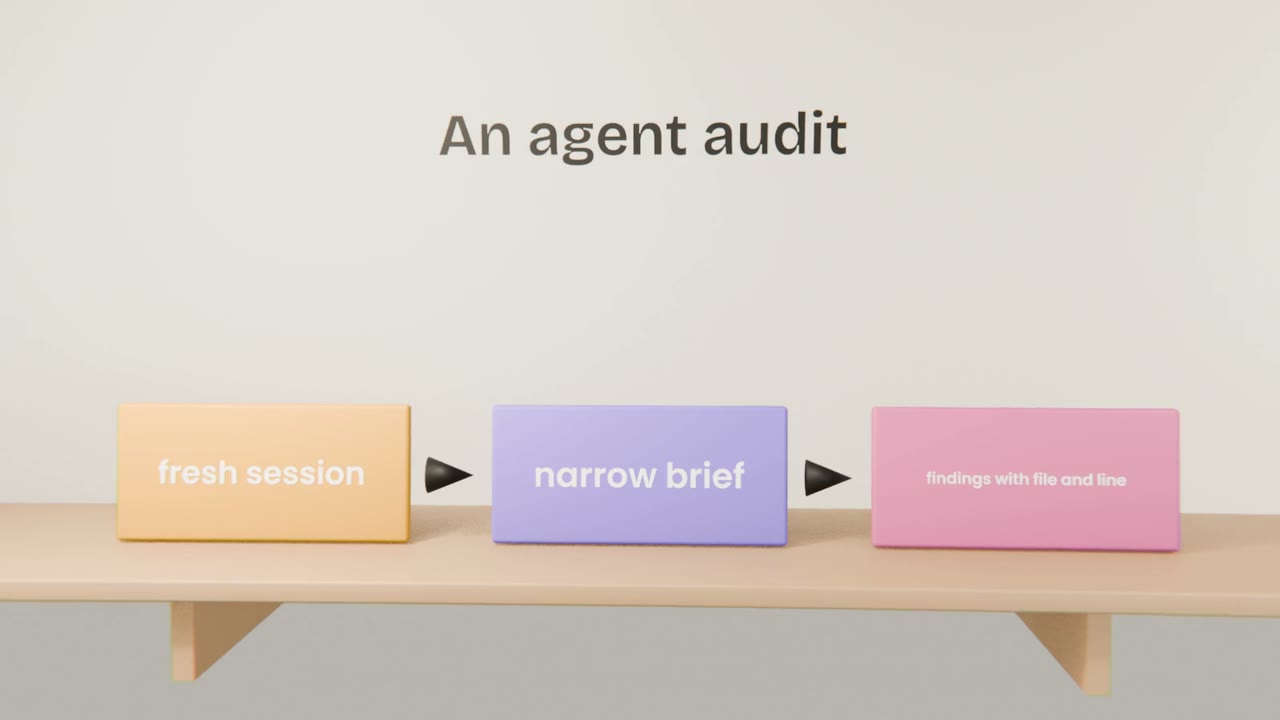
Running an agent audit
Fresh context
Not the session that wrote the code.
One area at a time
"Find missing authorisation checks."
Demand evidence
File, line and a way to reproduce.
Verify before fixing
Some findings will be false.
Run the pre-launch review
Go through the checklist, run a dependency audit, and run an agent audit per area. Record findings, verify them, and fix everything of high severity.
Done when
Your app is tested and locked down, ready to deploy.
Keep these
- Review by area.
- Audit dependencies.
- Verify agent findings before acting.